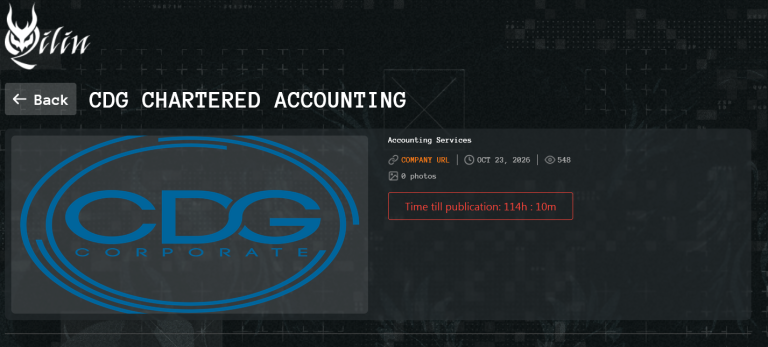
The Qilin ransomware group has listed Australian accounting firm CDG Chartered Accounting on its ransomware leak site, identifying the company’s website as cdgaccounting.com.au.
The listing is the third Australian company claimed by Qilin in the past two days, highlighting the continued threat posed by the ransomware operation to businesses across Australia and the wider Australasian region.
At the time of reporting, the group’s countdown indicated that CDG Chartered Accounting had just over 110 hours remaining before the alleged data is due to be published.
What Data Has Been Taken?
Qilin has not provided any evidence on its leak site detailing the alleged compromise. No information has been published about the type or volume of data reportedly stolen, and the extent of any potential exposure remains unknown.
As a result, the listing should be treated as an unverified claim by the threat actor until further evidence becomes available.
About CDG Chartered Accounting
CDG Chartered Accounting is an Australian accounting and professional services business operating through cdgaccounting.com.au. As an accounting firm, its business activities fall within a sector that can hold sensitive financial, tax and business information on behalf of clients.
The potential sensitivity of such information makes ransomware-related data theft a concern, although there is currently no evidence confirming what information, if any, Qilin has obtained in this case.
Qilin is a ransomware-as-a-service operation known for using threats of data publication to pressure victims into paying a ransom. Its latest Australian listings reinforce the importance of monitoring ransomware activity and maintaining effective security controls.
Further details may emerge if Qilin publishes evidence or CDG Chartered Accounting releases a statement.