Qilin ransomware continues to pose a significant threat to Australian organisations, with recent claimed victims spanning retail, non-profit services, technology, finance, construction and healthcare.
Qilin operates a ransomware-as-a-service (RaaS) model. MITRE ATT&CK identifies Qilin as an active ransomware family associated with Agenda and notes its ability to target Windows, Linux and VMware ESXi environments.
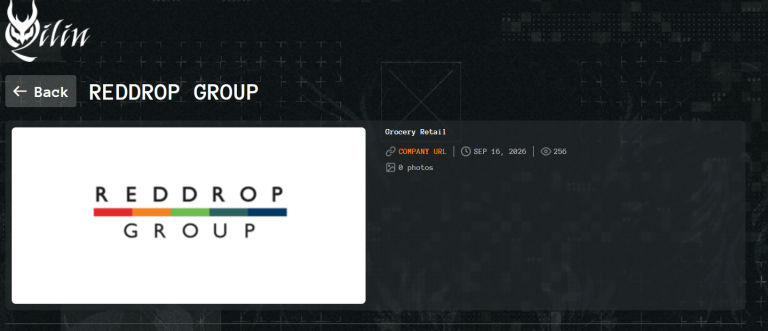
Recent Australian claims include Reddrop Group and Thorndale Foundation, both listed by Qilin in September. The Thorndale listing reportedly included samples such as passport photographs and invoices, while the Reddrop Group claim had no published evidence at the time of reporting. These remain threat-actor claims and should not automatically be treated as independently confirmed breaches.
The continued Australian activity is consistent with wider regional reporting. Group-IB identified Qilin as one of the most active ransomware operators in the ANZ region during Q2 2026, recording 11 attacks, while its August report again placed Qilin among the region’s most active operators.
Broad Targeting
Qilin’s victim profile is notably diverse. Its activity has affected organisations across healthcare, manufacturing, technology, financial services, retail, transportation, utilities and professional services. This makes the group relevant not only to large enterprises but also to Australian and New Zealand mid-market organisations.
Recent claims involving Australian organisations illustrate this breadth:
| Company | Domain | Date | Industry | Country |
|---|---|---|---|---|
| Reddrop Group | reddrop.com.au | 16 Sep 2026 | Retail | AU |
| Thorndale Foundation | thorndale.com.au | 15 Sep 2026 | Non-Profit | AU |
| DigiGround | digiground.com.au | 29 Aug 2026 | Software & IT Services | AU |
| The Frame Group | framegroup.com.au | 29 Aug 2026 | Software & IT Services | AU |
| Professional | prms.com | 21 Aug 2026 | Finance | AU |
| Asset Flooring Group Australia | assetflooring.com.au | 3 Aug 2026 | Construction | AU |
| Seed Outsourcing | seedoutsourcing.com | 3 Aug 2026 | Finance | AU |
| Pennant Hills Golf Club | pennanthillsgolfclub.com.au | 2 Jul 2026 | Sports / Hospitality | AU |
| The Banyans | thebanyans.com.au | 8 Jun 2026 | Healthcare | AU |
| Kinetic Education | kineticeducation.com.au | 8 Jun 2026 | Education | AU |
| Alpha Group NZ | alphagroup.nz | 24 May 2026 | Biotechnology / Healthcare / Manufacturing | NZ |
| Branded Products | brandedproducts.com.au | 24 May 2026 | Advertising | AU |
| Generation Life | genlife.com.au | 15 May 2026 | Finance / Investment | AU |
| Australian College of Business Intelligence | acbi.edu.au | 15 May 2026 | Education | AU |
| Menzies Group | menziesgroup.com.au | 15 May 2026 | Facilities / Cleaning Services | AU |
| Australian College | acbi.edu.au | 15 May 2026 | Education | AU |
| Bluize | bluize.com.au | 13 May 2026 | Hospitality / Gaming | AU |
| Construction Sciences | constructionsciences.net | 28 Apr 2026 | Construction / Engineering | AU |
| Tripod Farmers | tripodfarmers.com.au | 17 Apr 2026 | Food & Beverage / Agriculture | AU |
| Peuker & Alexander | peuker.com.au | 10 Apr 2026 | Construction / Manufacturing | AU |
| Seeing Machines | seeingmachines.com | 31 Mar 2026 | IT-Enabled Services | AU |
| Kennedy McLaughlin | kennedymclaughlin.com.au | 23 Mar 2026 | Accounting | AU |
| Fortress Resistors | fortressresistors.com | 10 Mar 2026 | Industrial Equipment | AU |
| Maintenance & Project Engineering | mpe.com.au | 22 Feb 2026 | Consulting / Asset Management | AU |
| Esperance Metaland | espmetaland.com.au | 21 Feb 2026 | Metals & Mining / Construction / Manufacturing | AU |
| Mt Barker Co-op | mtbarkercoop.com.au | 11 Feb 2026 | Retail | AU |
| Esperance Communications | ec.com.au | 30 Jan 2026 | Electronics / Software & IT Services | AU |
Dates and victim status reflect the supplied dataset. Leak-site listings are allegations by the threat actor unless independently confirmed.
Qilin Tradecraft
Qilin combines conventional ransomware deployment with extensive use of legitimate administration and remote-access functionality.
Reported techniques include:
- Valid accounts and credential theft for initial access and privilege escalation.
- Exploitation of public-facing applications and remote services.
- Phishing, including malicious attachments and links.
- PowerShell and command-line execution.
- RDP, SMB, SSH and WinRM for lateral movement.
- Cobalt Strike and other remote-access tooling.
- Chisel, Ngrok and other tunnelling mechanisms to maintain connectivity.
- Archive-based collection before data exfiltration.
- Defense impairment, including termination or modification of security tooling.
- Data exfiltration followed by encryption, supporting a double-extortion model.
MITRE ATT&CK documents Qilin’s use of PowerShell, exploitation of public-facing applications, SMB and SSH, remote-access software, process discovery and data encryption.
Qilin activity has also been associated with Agenda Ransomware, Qilin.B, NETXLOADER and SmokeLoader. Reported vulnerabilities associated with Qilin activity include CVE-2023-27532 and CVE-2024-1853, while separate 2026 reporting has linked Qilin activity to exploitation of CVE-2026-20079 and CVE-2026-20316 in Cisco Secure Firewall Management Center.
MITRE ATT&CK Techniques
| Technique | ID | Description / Qilin association |
|---|---|---|
| Exploit Public-Facing Application | T1190 | Exploitation of externally accessible applications and interfaces |
| Exploitation for Client Execution | T1203 | Exploitation of vulnerabilities for execution |
| Phishing: Spearphishing Attachment | T1566.001 | Malicious attachments used for initial access |
| Phishing: Spearphishing Link | T1566.002 | Malicious links used for initial access |
| External Remote Services | T1133 | Use of externally accessible remote services |
| Remote Services | T1021 | Lateral movement through remote services |
| RDP | T1021.004 | Remote Desktop Protocol |
| PowerShell | T1059.001 | PowerShell-based execution and discovery |
| Valid Accounts | T1078 | Abuse of legitimate credentials |
| Network Service Scanning | T1046 | Discovery of network services |
| Remote Access Software | T1219 | Remote-management and access tooling |
| Brute Force | T1110 | Credential attacks |
| System Network Configuration Discovery | T1016 | Network discovery |
| Data Encrypted for Impact | T1486 | Encryption of victim systems and data |
| Application Layer Protocol: Web Protocols | T1071.001 |