New Zealand medical technology company Fisher & Paykel Healthcare has disclosed unauthorised access to two employee email accounts and a subset of company files following a cyber security incident.
In a statement published on its website, the company said it had activated its incident response procedures and launched an investigation into the nature and extent of the unauthorised activity.
The company confirmed that some of the accessed files contained personally identifiable information (PII), with affected individuals being notified. Relevant authorities have also been informed.
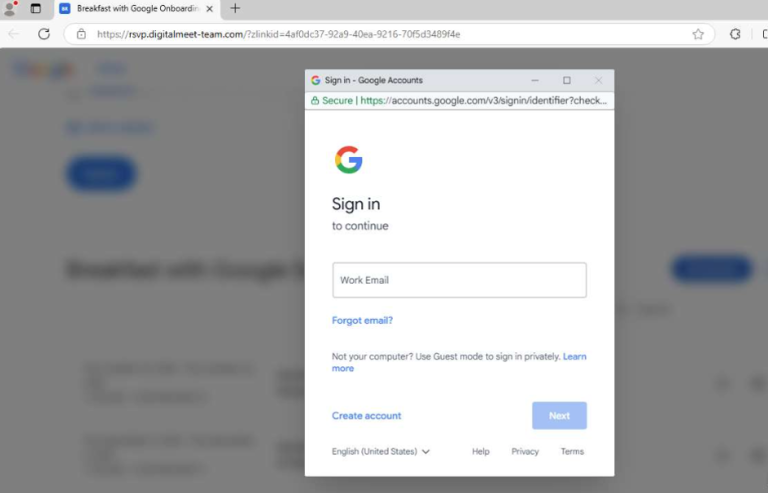
While Fisher & Paykel Healthcare has not disclosed the suspected initial access method, the compromise of employee email accounts is consistent with a potential phishing or credential-compromise incident. However, the company has not confirmed that phishing was involved.
The company stated that it had found no evidence of ransomware or malware and believed the incident had been contained. It also confirmed there was no impact on its products, manufacturing operations or supply chain, and no evidence that the systems maintaining patient data had been compromised.
Fisher & Paykel Healthcare does not expect the incident to have a material impact on its financial performance or operations.
The incident highlights how access to employee email accounts and associated files can expose sensitive information, even when core business operations and patient data systems remain unaffected. Organisations should continue to prioritise phishing-resistant authentication, monitoring of suspicious email account activity, and controls limiting access to sensitive files.
Source: Fisher & Paykel Healthcare – Statement regarding cyber incident