The New Zealand Defence Force (NZDF) has confirmed a cyber security incident involving the compromise of a database associated with its Force4Families Defence Discounts scheme, potentially exposing the personal information of registered users.
The incident, reported on 20 November 2026 by Stuff and Radio New Zealand (RNZ), has resulted in affected websites being taken offline while NZDF investigates the compromise.
What happened?
NZDF has confirmed that preliminary investigations indicate a database associated with the Force4Families Defence Discounts scheme was accessed without authorisation.
The database reportedly contained personal information belonging to registered users, including:
- Names
- Email addresses
While the confirmed information disclosed so far appears limited to names and email addresses, the incident raises concerns about the potential exposure of information relating to serving Defence Force personnel and their families.
The Force4Families scheme is associated with providing eligible Defence personnel and their families access to discounts and benefits.
NZDF has removed the affected websites from service as investigations continue.
Why is this concerning?
Although the information identified so far may appear relatively limited, the context of the database makes this incident particularly concerning.
Personal information associated with Defence Force personnel and their families can be valuable to cybercriminals and potentially more sophisticated threat actors.
Names and email addresses can be used to develop convincing, targeted phishing campaigns, particularly where attackers can associate individuals with the New Zealand Defence Force.
There is currently no confirmation that additional sensitive information, military operational information or classified Defence material has been accessed.
A reminder about the risks of third-party websites
The incident also highlights the security risks associated with websites and services operating outside an organisation’s primary operational environment.
Even where a website is not directly involved in military operations, databases supporting employee benefits, family services and other administrative functions can contain information that may be attractive to attackers.
Organisations need to ensure these supporting services receive the same appropriate security oversight as their primary corporate and operational systems.
It is not known how the site has been compromised but the technologies behind it line up with the overnight PHP and nginx vulnerabilities released.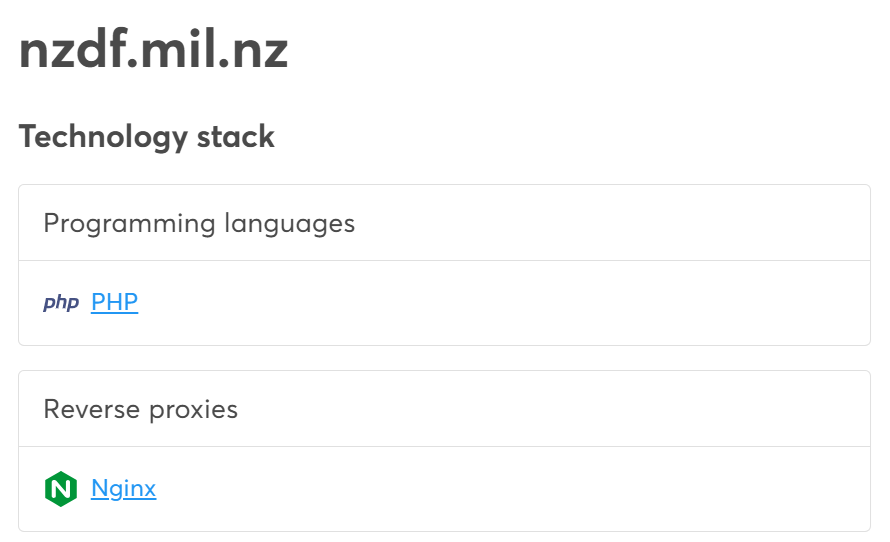
What should affected users do?
Individuals registered with the Force4Families scheme should remain alert to unexpected emails, messages or phone calls referencing NZDF, Defence discounts or associated services.
Recommended precautions include:
- Be cautious of unexpected emails asking you to verify account details or provide personal information.
- Avoid clicking links in unsolicited messages, even where they appear to reference legitimate Defence-related services.
- Do not provide passwords, authentication codes or other sensitive information in response to unexpected requests.
- Use unique passwords and enable multifactor authentication (MFA) on relevant accounts.
- Verify suspicious communications directly through official NZDF channels.
Investigation ongoing
NZDF has confirmed the database compromise and taken the affected websites offline while it investigates.
At this stage, the full extent of the incident, how the attackers obtained access and whether information has been extracted or subsequently misused remain unclear.
The incident is another reminder that personal information held by government agencies and their supporting services can present an attractive target, even when the systems involved are not directly connected to sensitive operational environments.