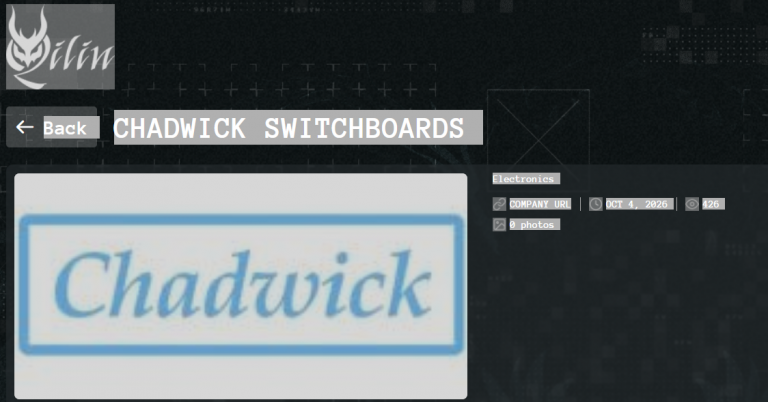
Australian switchboard manufacturer Chadwick Switchboards has been listed on the ransomware leak site operated by the Qilin ransomware group.
The listing was first observed on 4 October 2026, with Chadwick Switchboards identified as an Australian manufacturing victim.
Chadwick Switchboards is a Western Sydney-based company that has operated since 1942 and specialises in the design, manufacture, commissioning and maintenance of low-voltage electrical switchboards for the building, construction, industrial and infrastructure sectors.
No details or evidence of compromise
At this stage, however, the Qilin listing provides no details about the alleged incident. There is no stated volume of data, description of the information supposedly obtained, ransom deadline or samples of allegedly stolen files.
Importantly, there is also currently no independently available evidence confirming that Chadwick Switchboards has been compromised.
A ransomware group placing an organisation on its leak site should therefore be treated as an unverified claim, rather than confirmation that an intrusion or data theft has occurred.
This distinction is particularly important with ransomware leak sites. Groups such as Qilin have an incentive to publicly claim victims and use the threat of data publication as part of their extortion operations. Qilin has previously been associated with significant data-theft and double-extortion activity.
For Chadwick Switchboards, the next indicators to watch will be whether Qilin subsequently adds data samples or additional claims, whether Chadwick makes a public statement, or whether independent reporting provides evidence supporting the allegation.
For now, the appropriate description is simple: Qilin has listed Chadwick Switchboards as a victim, but there is no published evidence of compromise or data theft at this time.
For more information on Qilin see our article here