A Security Operations Centre (SOC) and Security Information and Event Management (SIEM) platform can be incredibly powerful...
siem
What Is Threat-Informed Defence? Threat-Informed Defence (TID) is the systematic application of an understanding of adversary tactics,...
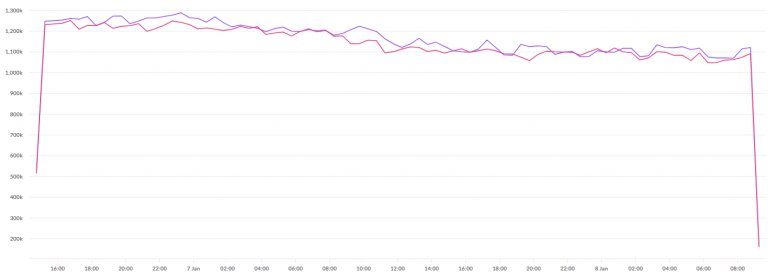
Over the past several months, I observed a recurring issue affecting a number of Windows-based Logstash data...
Trend Agentic AI SIEM The Trend Agentic AI SIEM agent is another example of a company rushing...

If you have data in a nested table array you can convert it to the standard key:value...
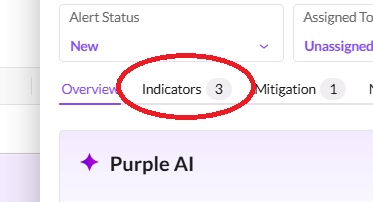
Ever wondered how you get the indicator tab in the SentinelOne AI SIEM alerts populated? Sadly the...
Endpoint URL: https://{your sentinelone console domain}/web/api/v2.1/threat-intelligence/iocs Headers Required: Authorization Content-Type Official Documentation: https://{your sentinelone console domain}/new-api-docs ...

Why Should You Manage Your Log Ingestion? Cost Implications SIEM tools operate under a licensing model that...
There are different options for parsing data in Microsoft Sentinel. Query time parsing when the parsing is...
Microsoft have an API to add IOCs to the threat intelligence module in sentinel which can you...