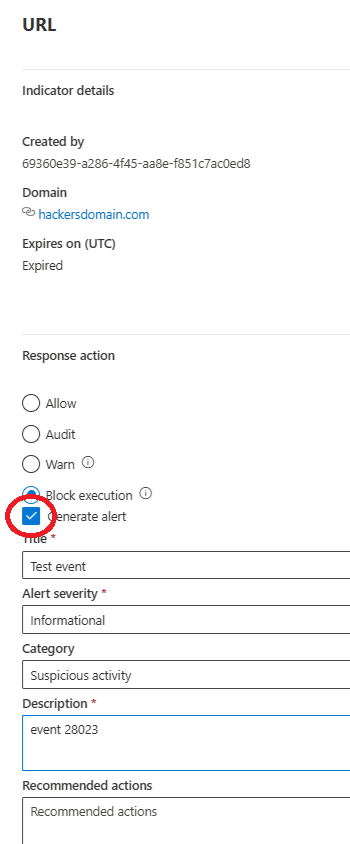
No matter how hard I try, I cannot get the Microsoft Defender Indicator API https://api.securitycenter.microsoft.com/api/indicators/import to import...
threatinfo

To integrate Nifi with an Azure Key Vault follow the below steps Step 1 – Add Parameter...
User names used by actor seen using VPNs with Canadian source IP addresses 10/05/2024. Replace targetDomain below...

Why Should You Manage Your Log Ingestion? Cost Implications SIEM tools operate under a licensing model that...
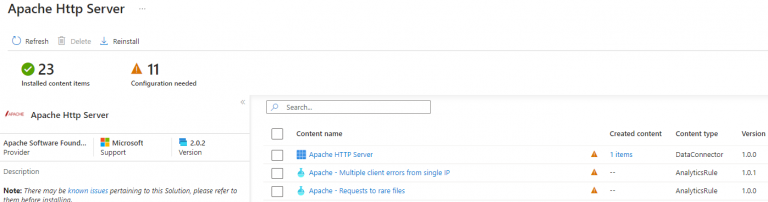
There are different options for parsing data in Microsoft Sentinel. Query time parsing when the parsing is...
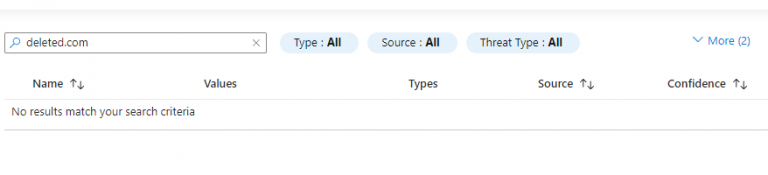
Microsoft have an API to add IOCs to the threat intelligence module in sentinel which can you...
MISP MYSQL database growing too large and starting to get out of control? API calls getting slower...

If you receive a “An internal error has occured” error message when clicking on various menu functions...

A threat activity cluster is a grouping of security alerts which are related to a unique or similar activity...

I was using filebeat to listen on port 514 to accept rsyslog messages from AIX servers with...