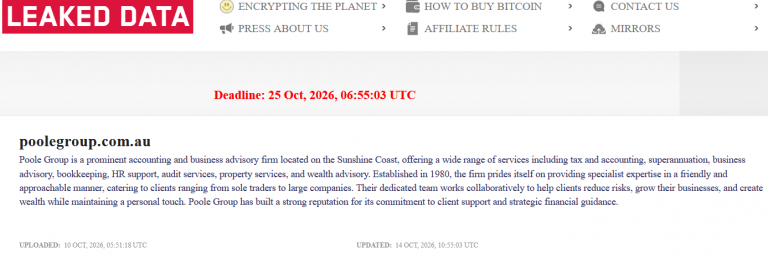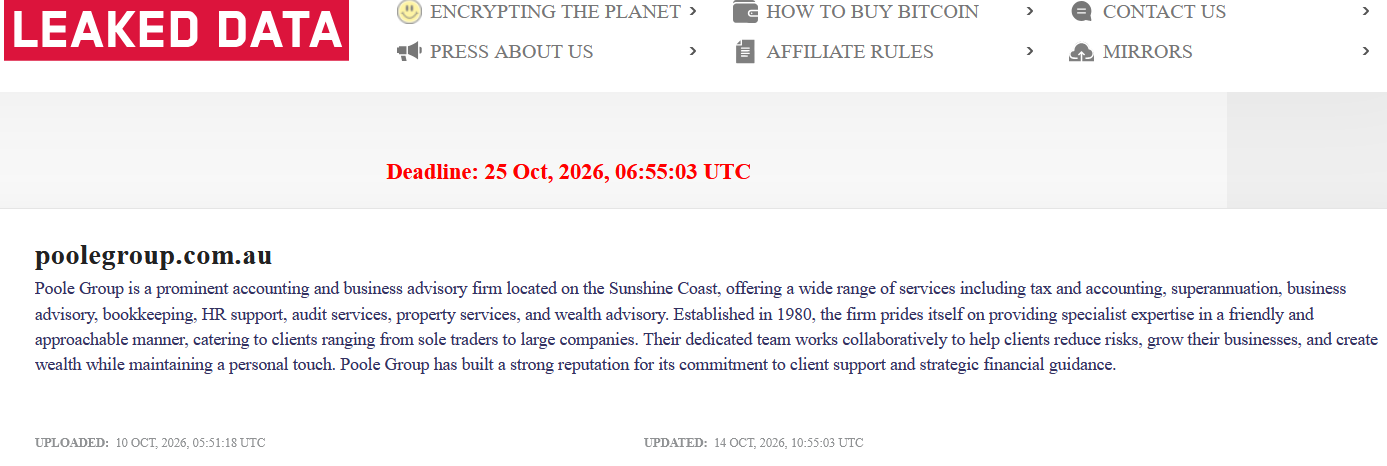
Australian accounting and business advisory firm Poole Group (poolgroup.com.au) has been listed on the LockBit 5 ransomware group’s leak site. Further information about the alleged incident is expected to emerge.
At this stage, the listing should be treated as an unverified claim by the threat actors. No independently verified details are available regarding the potential scope of the incident, whether data has been stolen, or whether systems have been encrypted.
Other Australian LockBit 5 Victims in 2026
Poole Group is the latest Australian organisation to appear on LockBit 5’s victim listings. Other Australian organisations reported as listed by the group during 2026 include:
- Vitex Pharmaceuticals (vitexpharma.com) – an Australian contract manufacturer of vitamins and nutritional supplements, reportedly listed in April.
- Charlie Bears (charliebears.com.au) – the Australian teddy bear and collectable toy business, reported as a LockBit victim in April.
- Aeromedical Society of Australasia (aeromedsocaustralasia.org) – a professional organisation serving the aeromedical community across Australia and New Zealand, listed in February.
These listings demonstrate the breadth of organisations appearing in LockBit 5’s claimed victim activity, spanning pharmaceuticals, retail and the aeromedical sector. However, a listing alone does not establish the extent of a compromise or confirm that data has been exfiltrated. The Aeromedical Society of Australasia publicly acknowledged the group’s claims and said it had contacted its contracted provider and relevant authorities.
Who Are LockBit and LockBit 5?
LockBit is a financially motivated ransomware-as-a-service (RaaS) operation that has historically relied on affiliates to compromise organisations, steal data and deploy ransomware. Its operations suffered a significant disruption in February 2024 following an international law enforcement operation known as Operation Cronos.
The LockBit 5.0 iteration emerged in late 2025 as the operation sought to rebuild its presence. It has since been associated with further victim claims and data-extortion activity. The group uses public leak-site listings to pressure organisations into engaging with its operators, with threats to publish allegedly stolen information. They have been fairly active this year with at least 10 victims each month being added.
ThreatIntel.co.nz will provide further updates on the Poole Group listing as more information becomes available.