The most commonly probed ports during November are a continuation of what we have been seeing.
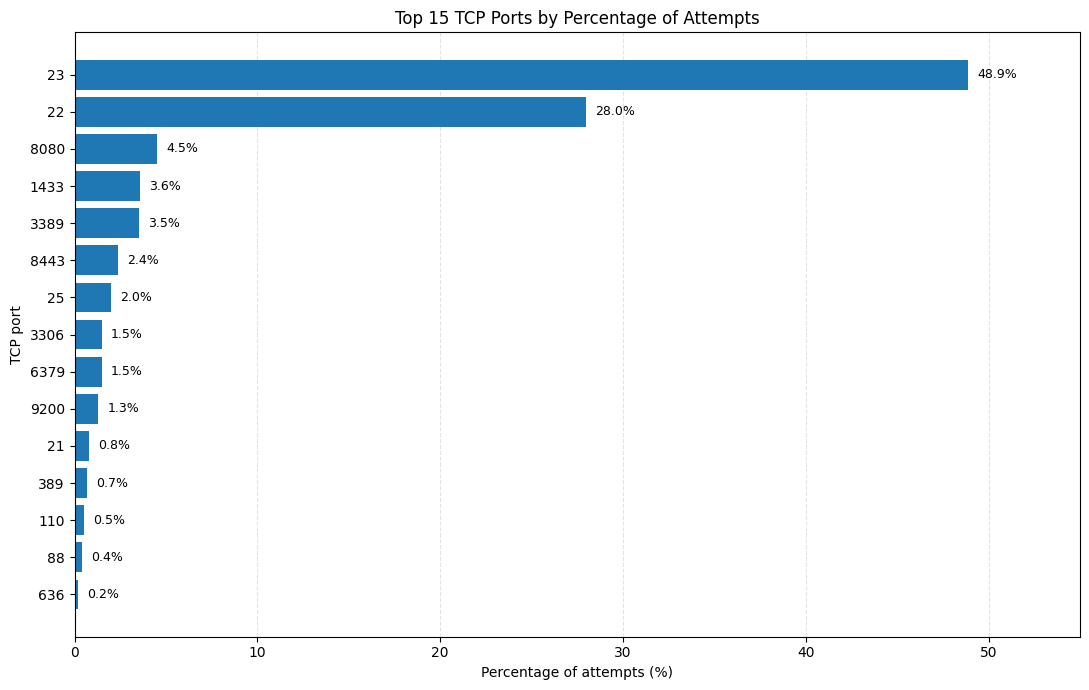
Telnet keeps the top spot and significantly increases its lead on SSH in second spot. Botnet traffic appears to be growing.
The remaining 13 spots are quite consistent with past sightings with only a couple change positions.
Again, these are the top ports attempted. Changing your service to a random high number port does not protect it, it may receive less attempts but it will receive attempts. The plethora of super questionable ‘legitimate’ online scanner services being used by Threat actor groups will find it and do their best to cook it like a French Super Market Freezer.