Supermarkets across the US, Europe, Australia and New Zealand are facing an apparent increase in malicious cyber activity, spanning exposed refrigeration systems, ransomware claims and fraudulent customer promotions.
One concerning development involves suspected Russian targeting of internet-exposed refrigeration controllers across Europe. Industrial control systems left accessible from the internet can create opportunities for disruption, particularly when they lack adequate security controls. The reported activity highlights the potential for cyber incidents to affect more than IT systems, extending into the physical infrastructure that keeps supermarket operations running.
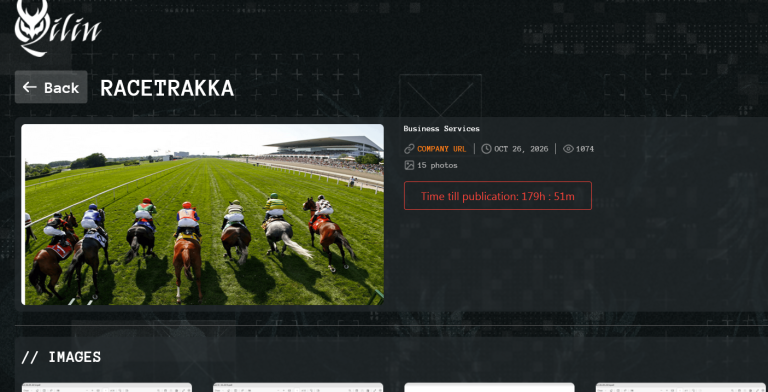
At the same time, giant retailer Ahold Delhaize experienced an outage affecting online services across many of their US brands, while ransomware group Qilin claimed Italian supermarket cooperative brand Coop Italia (coop.it) as a victim. Other recent supermarket-related incidents and claims include Diarco in Argentina, claimed by INC Ransom, alongside Australian retail entities Reddrop Group and Jones the Grocer. Again INC Ransom and Qilin are organised Russian linked groups operating heavily in Australasia.
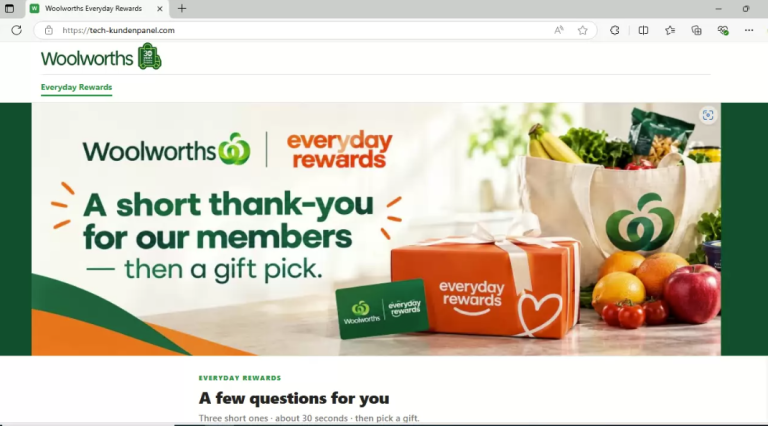
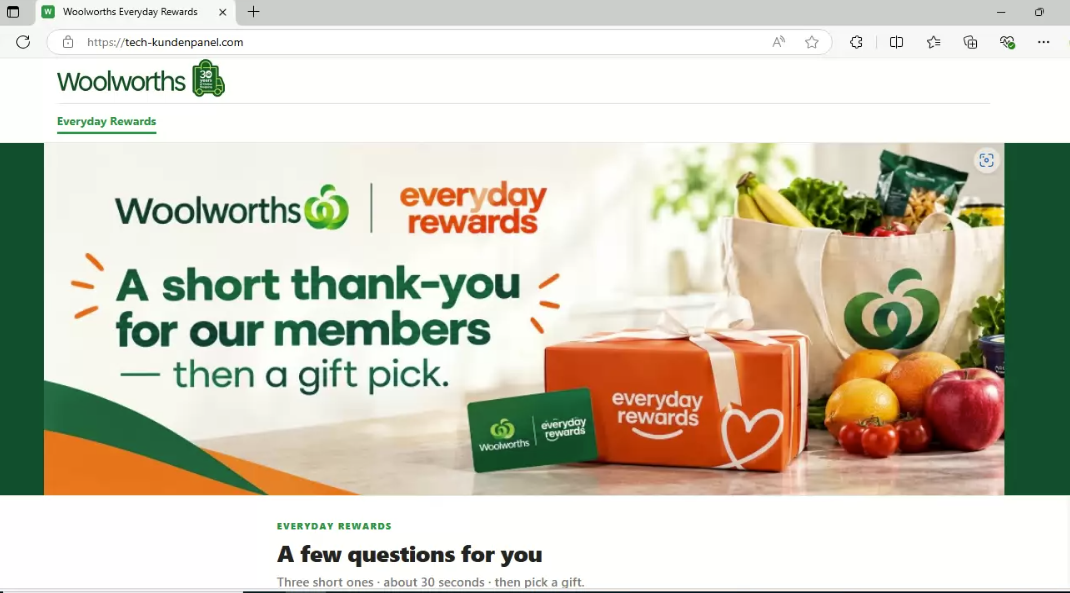
New Zealand shoppers are also being targeted through scams impersonating Pak and Save and Woolworths. These campaigns use supposed holiday promotions, surveys and rewards to lure customers into providing payment-card details. Victims may be promised an unusually generous gift in exchange for completing a short survey, before being asked to pay a seemingly insignificant $2.99 postage fee. The small charge is used to make the request appear credible while harvesting financial information. Some of these campaigns have been assessed as potentially linked to Chinese-backed scam operations, although attribution requires caution.
Why supermarkets are an attractive target
A possible motivation behind the increased attention is straightforward: supermarkets are cash-flow businesses that depend on continuous operations. If a cyber incident disrupts checkout systems, online ordering, refrigeration or supply-chain processes, transactions can stop and revenue can quickly be affected. Even a short interruption can create operational pressure, food-safety concerns and reputational damage.
For criminal groups pursuing financial extortion, this operational dependence may provide leverage. Meanwhile, fraudulent promotions offer another route to monetisation by exploiting customer trust in familiar retail brands.
Supermarkets should therefore consider cyber resilience across both corporate IT and operational technology. Internet-facing industrial controllers should be identified and secured, remote access tightly restricted, backups and recovery procedures tested, and incident response plans designed around the loss of critical retail services. Customers should be reminded that unexpected prize offers and surveys requesting card details for small postage fees are common warning signs of fraud.
The recent activity does not establish a single coordinated campaign against the supermarket sector. However, the combination of infrastructure targeting, ransomware claims and retail-brand impersonation demonstrates the breadth of threats facing an industry where keeping systems running is directly tied to revenue.